ONE TEAM. ONE FIGHT.
Signed in as:
filler@godaddy.com
ONE TEAM. ONE FIGHT.
Signed in as:
filler@godaddy.com
DATA PROTECTION FOR THE MOST SENSITIVE DEFENSE APPLICATIONS
Every MEMKOR SSD is a Self-Encrypting Drive (SED), providing hardware-based AES-256 XTS encryption for data-at-rest.
But protecting mission data requires more than encryption alone. MEMKOR combines industry-standard SED management with configurable Write Protect, Data Elimination, security validation, and application-specific engineering to protect data from initial write through final sanitization.
AES-256 XTS | TCG OPAL 2.0 | SECURE ERASE | WRITE PROTECT | FIPS140
ENCRYPTION BUILT INTO THE DRIVE
MEMKOR Self-Encrypting Drives use hardware-based AES-256 XTS encryption to protect data written to NAND. Encryption and decryption occur within the storage device, providing data-at-rest protection without relying on host-based software encryption.
TCG OPAL 2.0 provides industry-standard security management on both SATA and PCIe/ NVMe platforms across the entire product line.
PROTECT THE DATA. ELIMINATE IT WHEN REQUIRED
Defense and Aerospace applications require more than just protecting data from unauthorized access. Mission data may also need to be protected against modification, then rapidly zeroized, securely erased, or sanitized depending on the program-specific requirements.
MEMKOR supports configurable hardware- and software-controlled security capabilities across the entire product line.
WRITE PROTECT
Prevent modification of stored data while maintaining controlled read access. Hardware and software Write Protect options can be configured around the application and system architecture.
CRYPTOGRAPHIC ERASE
Eliminate the crypto key protecting encrypted data, rendering the encrypted information inaccessible without requiring the NAND to be overwritten cell-by-cell. This method provides the fastest path to sanitization and allows the SSD to be returned to service quickly after the wipe operation.
FAST ERASE / ZEROIZE
Rapidly eliminate stored data using a device-level erase or overwrite process across the drive. Fast Erase takes longer than Cryptographic Erase, but completes significantly faster than the multi-pass military erase routines. A strong option when physical data overwrite is required while minimizing the time before the SSD can be returned to service.
MILITARY ERASE
MEMKOR supports configurable erase and sanitization routines for program-specific requirements, including applicable military and legacy erase methods such as:
NSA 9-12 | NSA 130-2 | DoD 5220.22-M | NAVSO P-5239-26 | AFSSI 5020
Additional erase sequences can be supported based on program requirements and storage architecture.
Crypto Erase | Fast Erase | Zeroize | Secure Erase | Military Erase | Hardware Trigger | Software Trigger
*Supported sanitization methods vary by product and configuration.
ONE DRIVE IS EASY. A SECURE SYSTEM IS DIFFERENT
Embedded systems may contain multiple SSDs, removable media, separate boot and mission-data drives, or storage distributed across VPX, XMC, and external architectures.
Managing credentials, initialization, unlocking, security state, and data elimination across multiple devices quickly becomes a system-level integration challenge, not simply an individual-drive feature.
MEMKOR has worked directly with Broadcom to develop firmware interoperability with MegaRAID SafeStore, enabling secure SED deployment within supported RAID architectures. Learn more.
SECURITY AT SYSTEM SCALE
Multiple SEDs | TCG Enterprise | Centralized SED Management | Pre-Boot Authentication | Authorization Acquisition | Embedded + Removable Storage
AUTHORIZATION ACQUISITION
MEMKOR SSDs can be integrated with supported third-party security management solutions to simplify authentication, policy implementation, and authorization acquisition for programs requiring additional security controls. Learn More
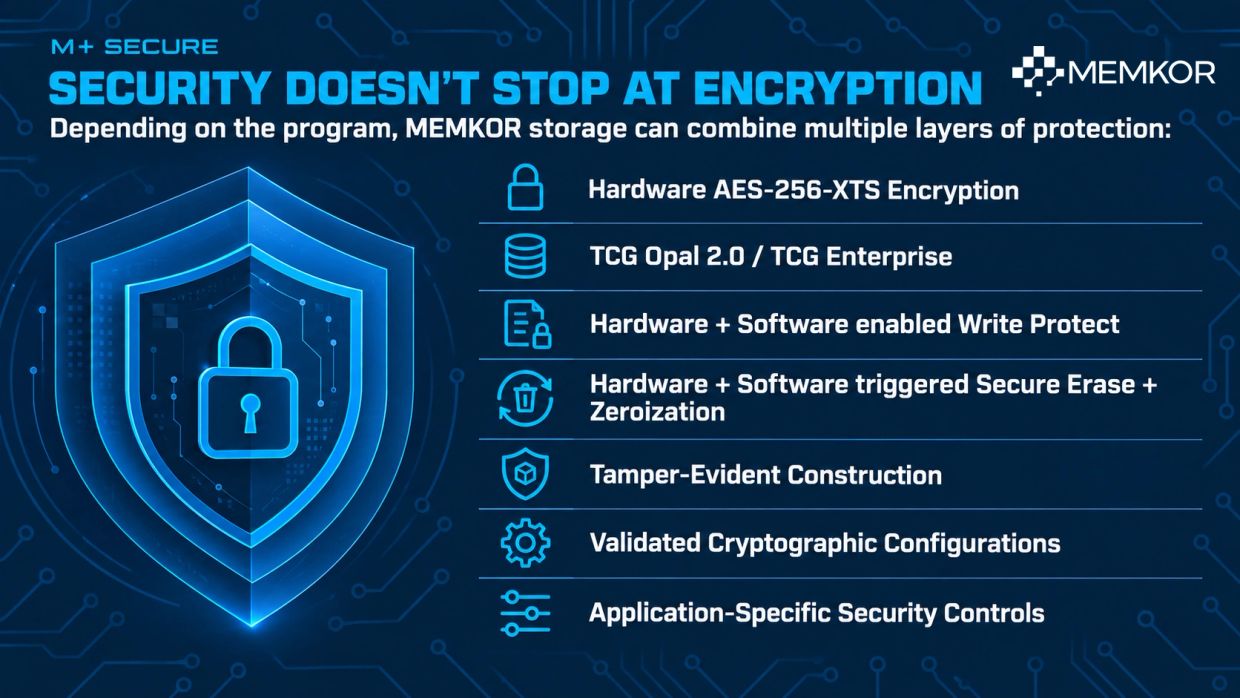
SECURITY DOESN'T STOP AT ENCRYPTION
Depending on the program, MEMKOR storage can combine multiple layers of protection:
SECURITY REQUIREMENTS DEFINES THE ARCHITECTURE
A boot SSD, removable mission-data module, multi-drive ISR recorder, unattended edge system, and embedded VPX computer can require very different approaches to authentication, Write Protect, Data Elimination, and security management.
MEMKOR works directly with system engineering and cybersecurity teams to configure storage around the program's security architecture, not simply enable a checklist of SSD features.
SECURITY IS AN INTEGRAL PART OF THE STORAGE ARCHITECTURE

3U VPX Storage
MEMKOR works with your team to optimize storage for your platform’s performance, power, capacity, security, and environmental requirements.
Configuration control and proactive obsolescence management help simplify qualification and support long program lifecycles.
Our engineering team supports your program throughout integration, qualification, production, and the product lifecycle.
We use cookies to analyze website traffic and optimize your website experience. By accepting our use of cookies, your data will be aggregated with all other user data.